Cloud key custody
Signing material lives only in a cloud HSM. Agents never export private keys to disk or memory as usable PKCS#12.
Cloud-backed virtual certificates
Liminal Keys publishes public certificates to your Mac and signs digests in cloud HSM custody. Admins run identities, devices, policy rules, and audit from Liminal Console.
How it works
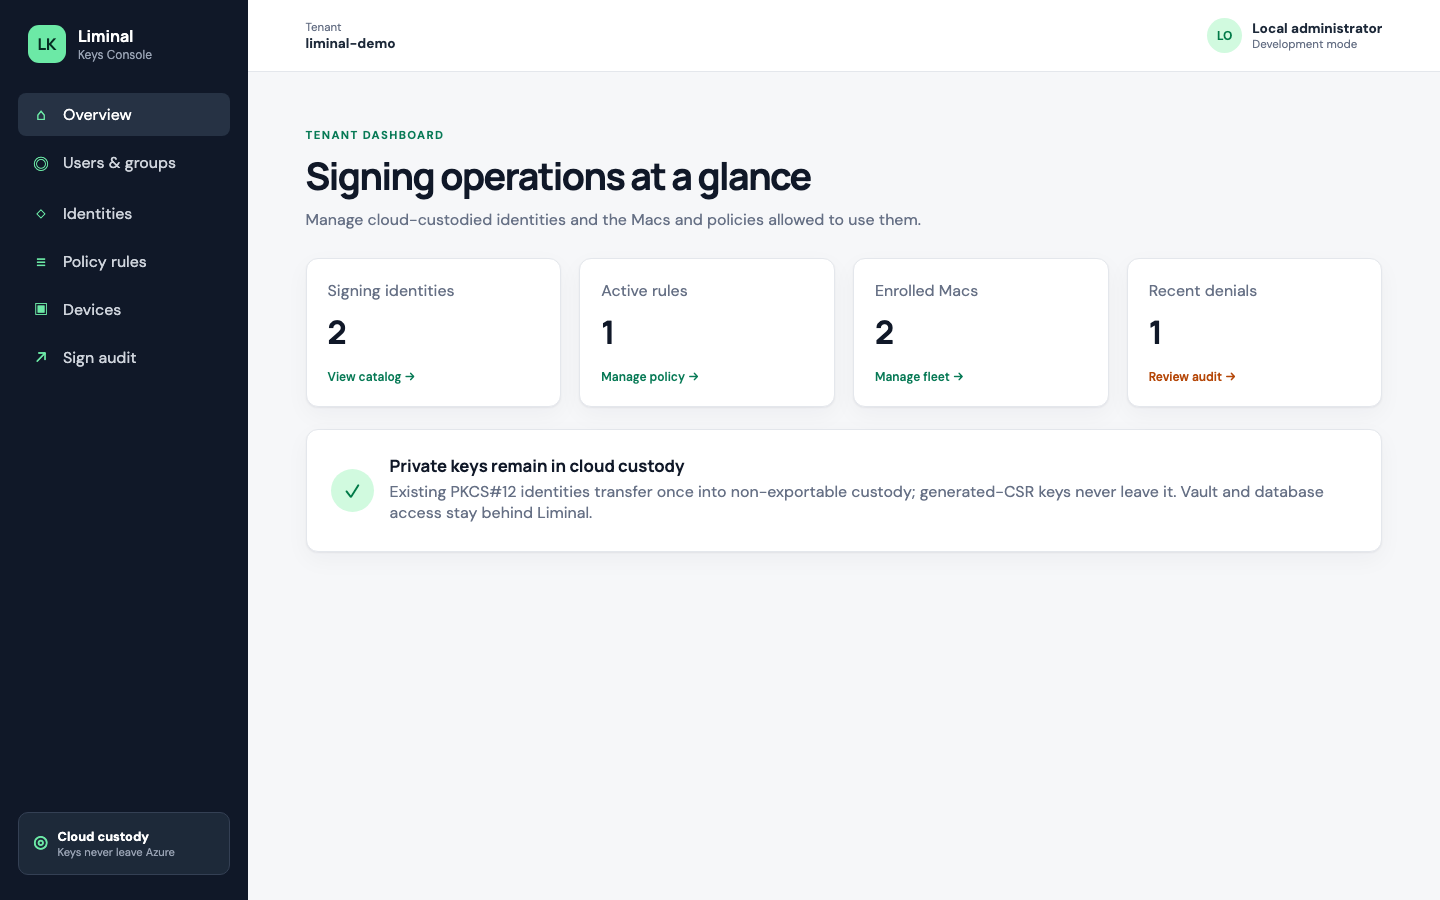
Private keys never leave cloud HSM custody. CryptoTokenKit handles local tooling; Console handles enrollment, policy rules, confirmation, and audit.
Signing material lives only in a cloud HSM. Agents never export private keys to disk or memory as usable PKCS#12.
The Mac publishes the public certificate and signs digests remotely when codesign or Xcode asks.
Enroll devices, define allow/deny policy with optional confirmation, and review sign audit from one tenant admin UI.
Existing PKCS#12 identities transfer once into non-exportable custody; generated-CSR keys never leave it.
Policy rules
Rules bind a signing identity to people, groups, and/or enrolled Macs for the sign operation. Enable or disable a rule, set an optional validity window, and require on-Mac confirmation before the signature is issued. Drafts do nothing until you Apply policy; conflicting allow and deny resolve to deny.
Console guide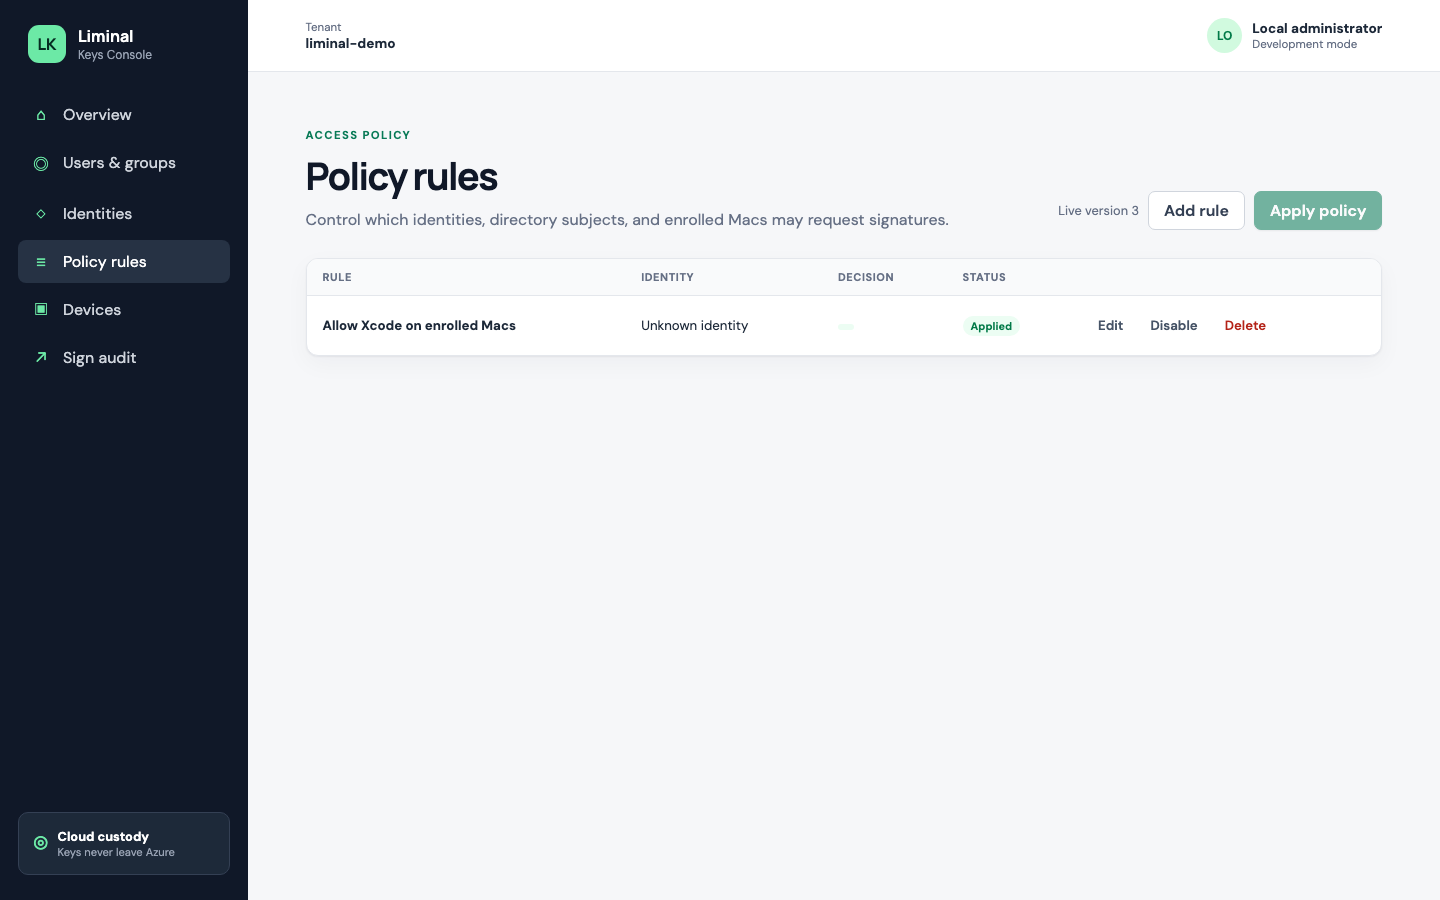
Identities & devices
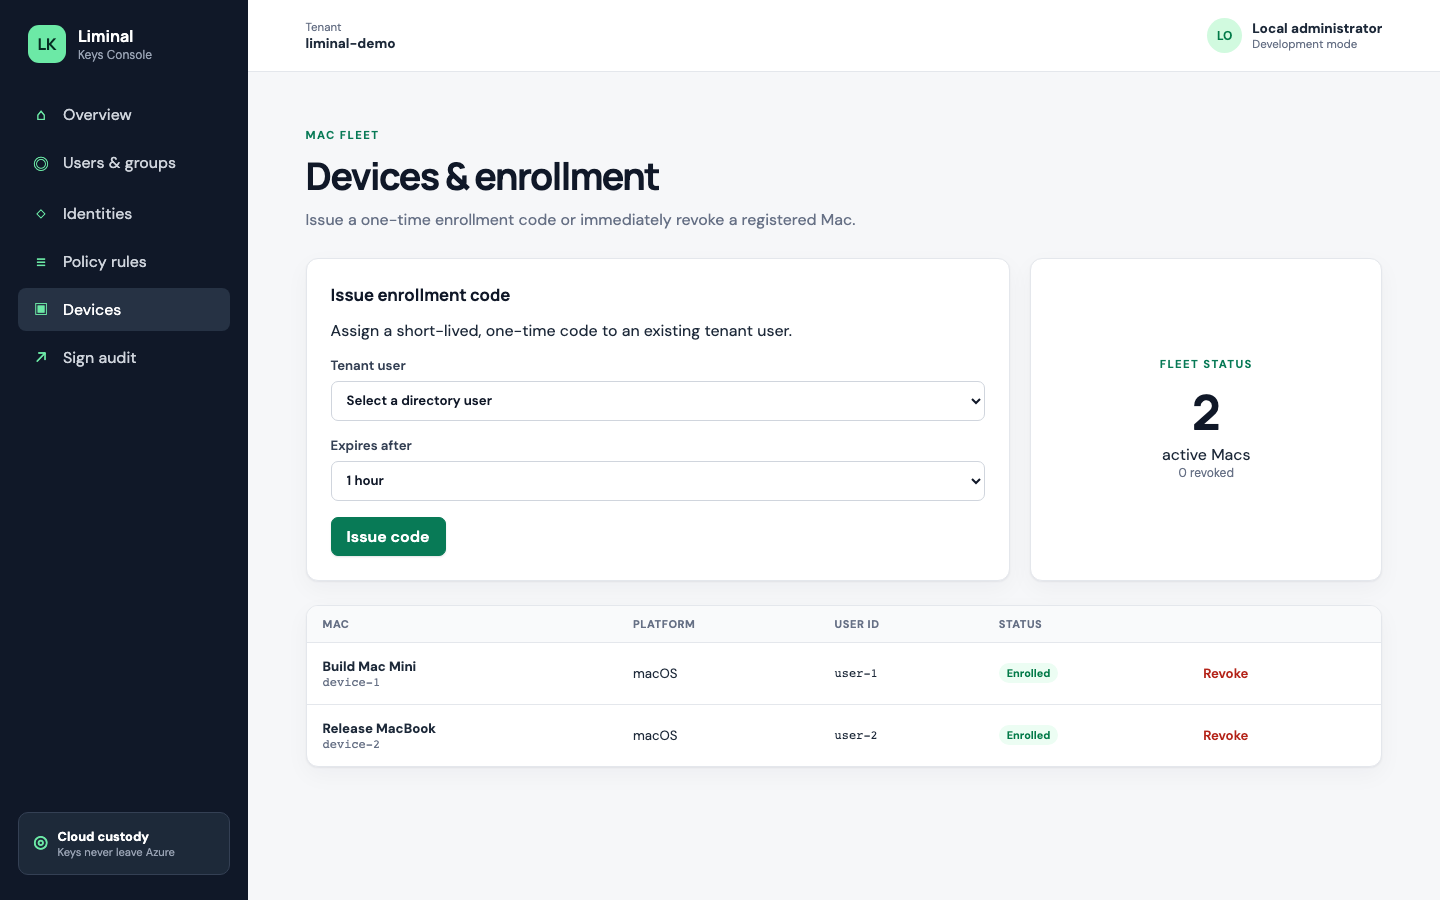
Onboard Apple signing identities in Console — import a PKCS#12 once into custody, or generate a CSR, complete it with the issued certificate, then apply policy. Issue short-lived enrollment codes so LiminalKeysHost can join the tenant fleet; revoke a device to stop signs immediately.
See product features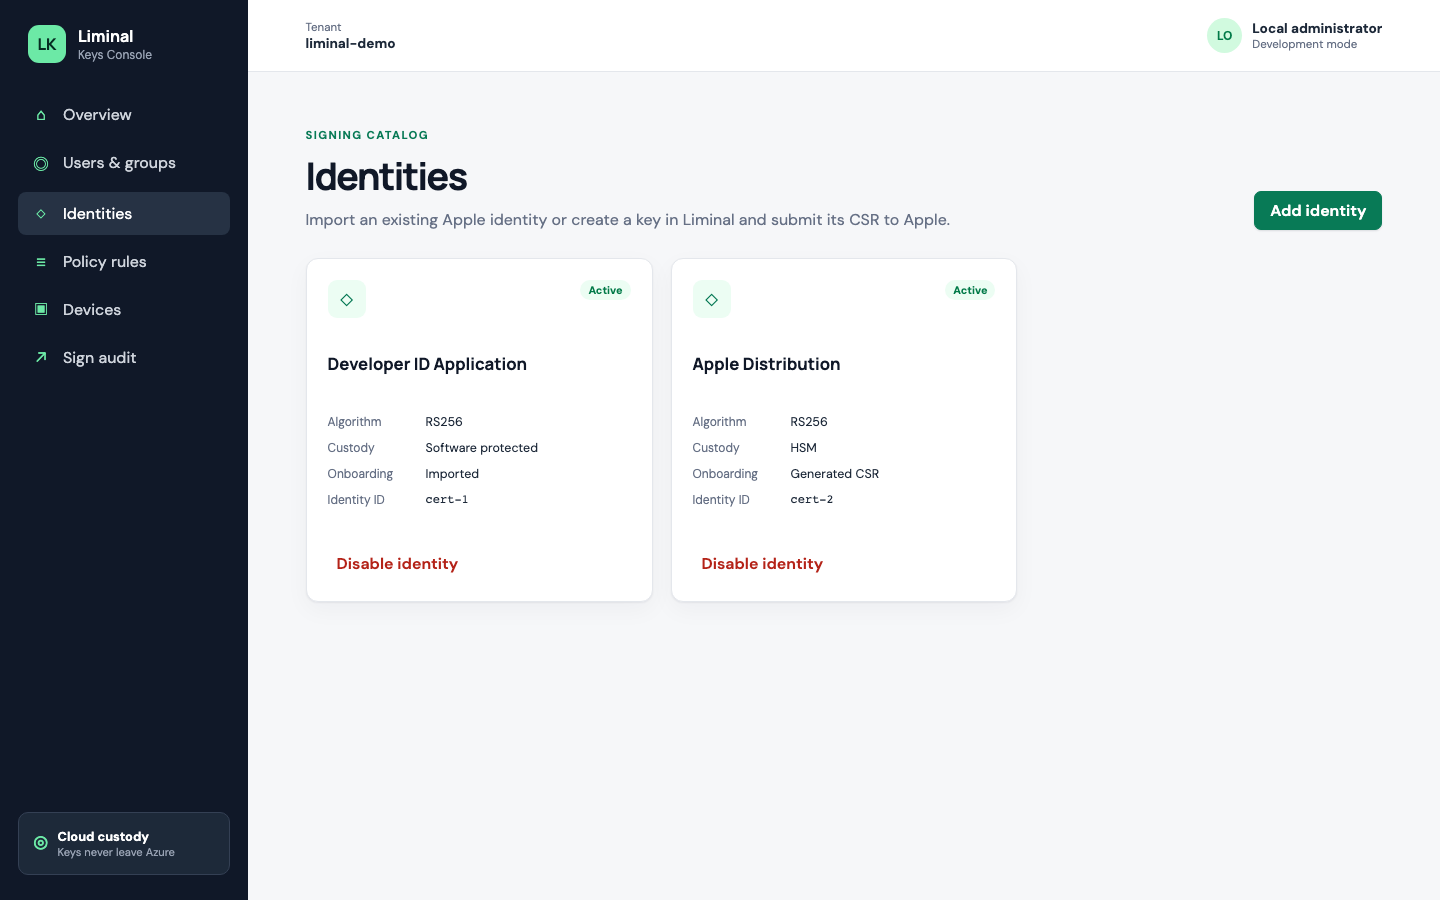
macOS signing flow
Set API URL to api.liminalkeys.com, paste the enrollment code, refresh
identities, and approve the CryptoTokenKit extension. When policy requires confirmation,
the host prompts before the digest is signed. Every allow or deny lands in the sign audit trail.
In production
A shipping Apple Watch and iPhone Teams client uses Liminal Keys so release signing keys stay in cloud custody — not on developer Macs.
Apple Watch + iPhone Teams client
Ship TestFlight builds without parking Apple signing private keys on laptops or sharing a PKCS#12 across the team.
Identities in Console, Mac enrollment, policy rules, and CryptoTokenKit on the signing machine — digests signed in cloud HSM custody.
TestFlight releases via this path, including build 1.7.0 — keys never left cloud custody on the Mac that signed.
Open Console, enroll a Mac, and sign against the live API at liminalkeys.com.